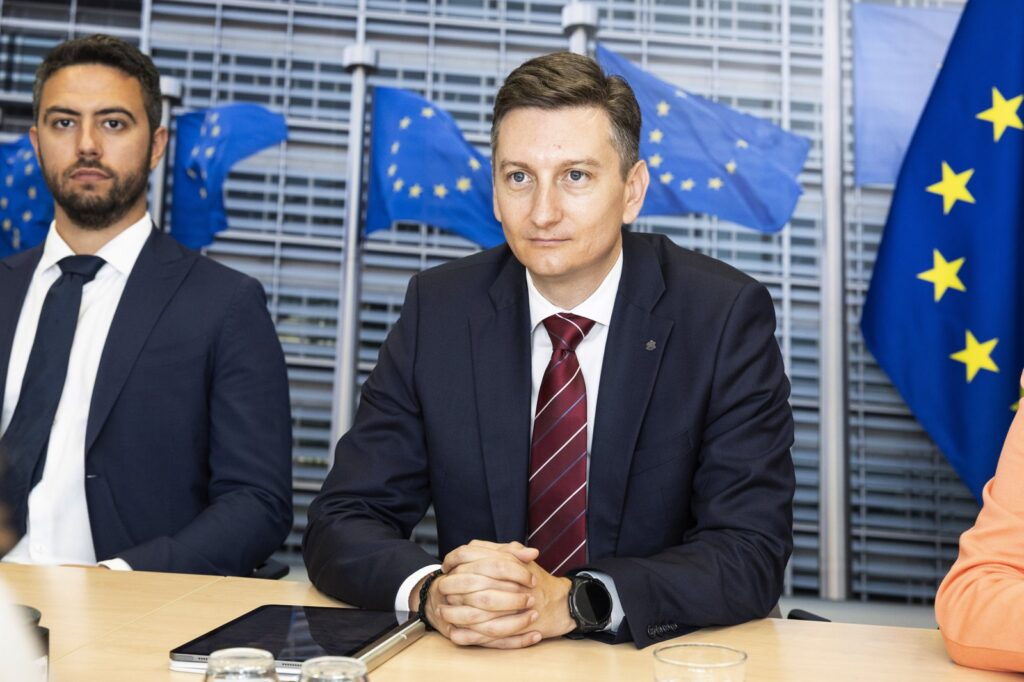
SOFIA, November 22, 2026 — Hackers maintained unauthorized access to Bulgarian government networks for nearly five years, stealing at least 130 gigabytes of documents equivalent to more than 62 million pages. Digital Minister Ivan Vasilev disclosed the breach at a cabinet briefing on November 18, calling it the longest and largest cyber espionage case ever recorded against the Bulgarian administration.
The breach in plain terms
Think of it like someone slipping into the building where every ministry drops its memos, reports and cabinet briefings, then photocopying the lot for five years without anyone noticing. The attackers targeted the document-exchange systems that state institutions use to share information with each other, moving between different parts of the infrastructure and gathering data on how the administration works, according to Reuters. The haul covers virtually every area of government work, including cabinet business, reports prepared by state institutions and correspondence between ministers and government bodies.
Here’s what it means for ordinary Bulgarians: investigators have found no evidence that citizens’ personal data — things like tax records, health information or identity numbers — was compromised, Vasilev said. None of the stolen documents have appeared on the dark web, the minister added. The operation bears the hallmarks of espionage rather than financially motivated cybercrime.
How it stayed hidden so long
The intrusion ran from 2021 through August 2026, spanning years of unstable coalition governments and repeated elections. Vasilev said the breach went undetected under successive administrations because the existing security tools never functioned as a single, integrated system. The practical upshot: hackers could move laterally across networks, collecting sensitive data on the functioning of the state, without triggering a unified alarm.
The breakthrough came in August 2026, after Bulgaria deployed a new national cybersecurity monitoring system. It flagged suspicious activity across government networks, prompting a large-scale technical investigation, the ministry said. Reuters reported that an August government statement confirmed the system had revealed long-term unauthorized activity.
Who was behind it
Vasilev said several international hacker groups accessed the systems, with activity traced to different locations around the world. He declined to identify specific countries of origin, stressing there is no conclusive evidence tying the attackers to a particular foreign government or intelligence service. “Whether they were serving the interests of these countries has not been established,” Vasilev told bTV in an interview reported by BTA on November 20. “We do not know what the hacking groups did with the information they extracted from the Bulgarian state.”
Investigators have not determined whether the hackers acted independently, as an organized operation, or on behalf of foreign intelligence, the minister said. The Prosecutor’s Office is now examining what state bodies did, and failed to do, over the past five years, including whether the breach resulted from deliberate negligence or possible assistance to the hackers.
Response and cleanup
Following the August discovery, authorities established a joint task force involving security and intelligence agencies, the defense and interior ministries, police and cybersecurity experts. The investigation has drawn on state-owned Information Services, private-sector specialists and international partners, including the European Union Agency for Cybersecurity (ENISA).
Authorities have terminated all identified unauthorized connections, isolated the affected infrastructure and removed malicious software from the systems. “We have successfully completed the third phase – the complete removal of the attackers from government systems,” Vasilev announced. The compromised environment will remain under enhanced monitoring for 90 days to detect any attempts by the attackers to regain access. Authorities are also tightening controls over administrator accounts and extending the national cybersecurity system to 28 municipal and regional administrations.
Context: a pattern of targeting
Bulgaria has been a repeated target of attacks blamed on Russia. In October 2022, the pro-Kremlin group KillNet claimed attacks that took down the websites of the presidency and several ministries, and the government site was hit again a month later. In 2023, the caretaker foreign minister said Russian hybrid attacks on Bulgaria had risen sharply. The latest revelations also revive memories of the massive National Revenue Agency breach in 2019, when hackers stole and leaked millions of files containing personal and financial information — arguably the country’s most significant cybersecurity scandal before this five-year intrusion came to light.
Sources
- Hackers took 62mn pages of Bulgarian government documents in five-year breach
- Hackers spied on the Bulgarian government for five years and stole 62 million pages of documents
- Hackers spent 5 years inside Bulgarian state networks, stealing 62 million pages of documents
- Bulgaria says hackers stole 62M pages of government documents
- Bulgaria says hackers stole 62 million pages of government documents
Photo: Lukasz Kobus (CC BY 4.0)