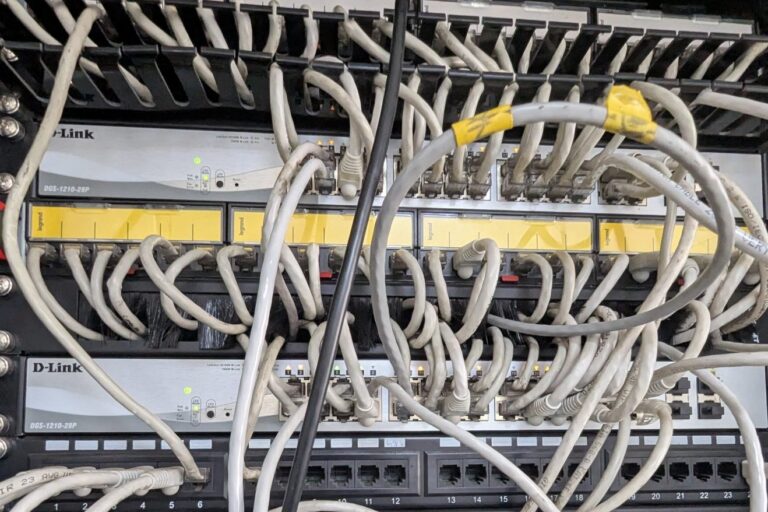
Japan’s Ministry of Health, Labour and Welfare has updated its 2026 guidelines to explicitly name Shadow IT as a starting point for cyber attacks in medical settings. The guidance treats unknown devices and services as unmonitored entrances for attackers and unmonitored exits for data.
What Shadow IT and Shadow AI Look Like in Hospitals
The ministry defines Shadow IT as equipment and software introduced and used without the management or permission of the IT department. In hospitals, the problem is structural. Small and medium-sized facilities often have only one or two information system staff members, or administrative staff handle the duties concurrently. Because the electronic medical record network is separated from the internet, transferring files and conducting remote work pushes staff toward unauthorised workarounds. Shadow AI expands this classic problem. Generative AI tools let employees bypass security approvals entirely, sending confidential data to external platforms one browser tab at a time.
Why They Are Prime Entry Points for Attackers
From an attacker’s perspective, a terminal or service the hospital does not know about is an entrance that no one is watching. It can just as easily become an exit that no one is watching for data exfiltration. The ministry’s management edition stresses that sharing procurement information across departments through committees is essential to prevent attacks via Shadow IT that planning managers do not grasp. The risk is not theoretical. Paubox survey data shows that seven in ten healthcare organisations have discovered AI-built tools handling patient data without IT or security knowing.
Numbers on Undiscovered AI Tools and Data Leaks
The scale of the hidden exposure is striking. Nearly nine in ten healthcare leaders say security or compliance staff always or usually review AI-written code that touches patient data before it goes live. Yet 70 percent have still found an AI-built tool handling that data outside IT’s view. Ninety-three percent of respondents confirm that real patient information reaches AI coding assistants during development, often sending data to the vendor before the tool is finalised. Seventy percent say this happens frequently or usually. More than half the leaders say AI-generated code has contributed to hardcoded credentials. About half say it has contributed to exposure of patient data or insecure data storage. Despite this, only half of surveyed hospitals have a written policy on AI coding assistants, even though 93 percent say they have trained at least some staff on safe use.
Steps to Discover, Replace and Govern Hidden Tech
The recommended mitigation is not elimination but identification and replacement. The ministry guidance argues for finding shadow elements and replacing them with solutions that are hard for attackers to exploit. Paubox advises setting one rule that test work uses synthetic data and enforcing it in the tools themselves, because training alone has not kept real patient data out of the assistants. SAP, announcing expanded agentic AI capabilities at its 2026 TechEd conference, acknowledged shadow AI as a major adoption challenge alongside cybersecurity and infrastructure maturity, highlighting the need for governance in enterprise AI deployments.
Creating a Culture Where Staff Report Early
To prevent new shadow elements from appearing, the ministry says it is essential to build a relationship where staff can consult the information-systems department at an early stage without fearing that consultation means the project will be stopped. The Paubox data illustrates the gap: a code review only covers what someone submits, and a check for a business associate agreement only happens if someone reports the connection. Unless someone tells IT the tool exists, it gets neither review nor contract.
Sources
- [For Medical Institutions] Cyber Attack Risks Posed by Shadow IT and Shadow AI|Yuta Morioka
- AI bubble
- Healthcare can't govern the AI tools it hasn't found yet – Help Net Security
- Sarah Webb, COO and Co-Founder of LawVu – Interview Series
- Techie Tonic: What is Shadow AI and why should IT worry?
- SAP stock: TechEd expands Joule and Business AI platform
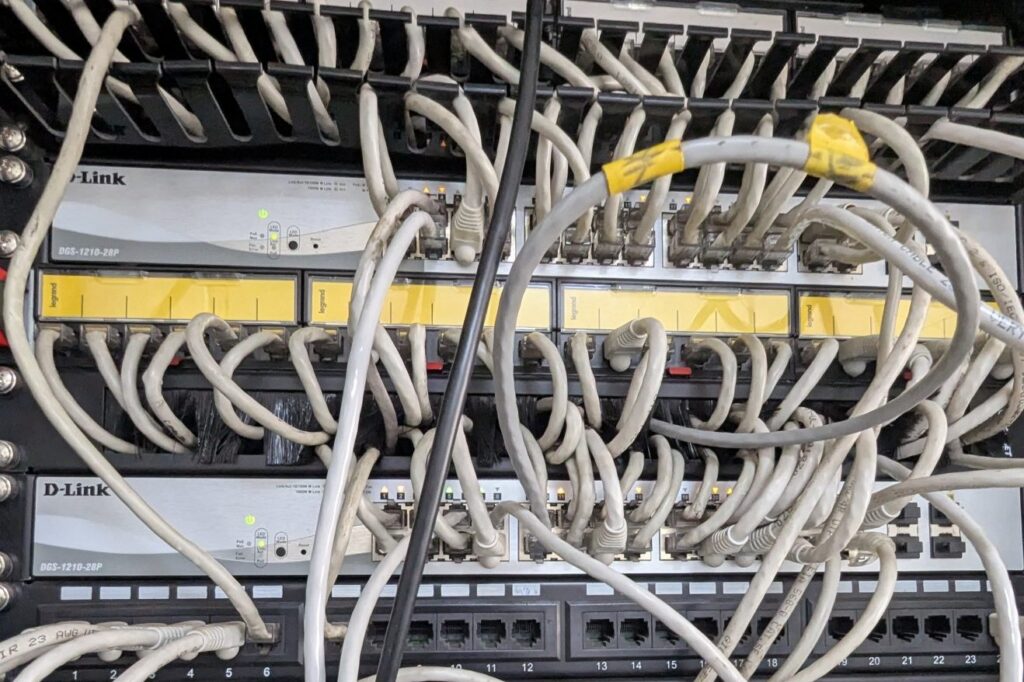
Photo: Moses Cursor Ssebunya / wordpress (CC CC0 1.0)