Q3 2026 Ransomware Surge Driven by NAS Flaws and Healthcare Targets
A 23% global ransomware spike in Q3 2026 is driven by attacks on unpatched Synology NAS devices and healthcare systems, exploiting known flaws and credential compromises.
The numbers are stark. About 70% of the fastest-impact events involved data exfiltration, and 84.1% of privilege escalation activity relied on a vulnerable driver. Attacker activity peaks at 11:00AM local time, with 63.3% of alerts landing during business hours.
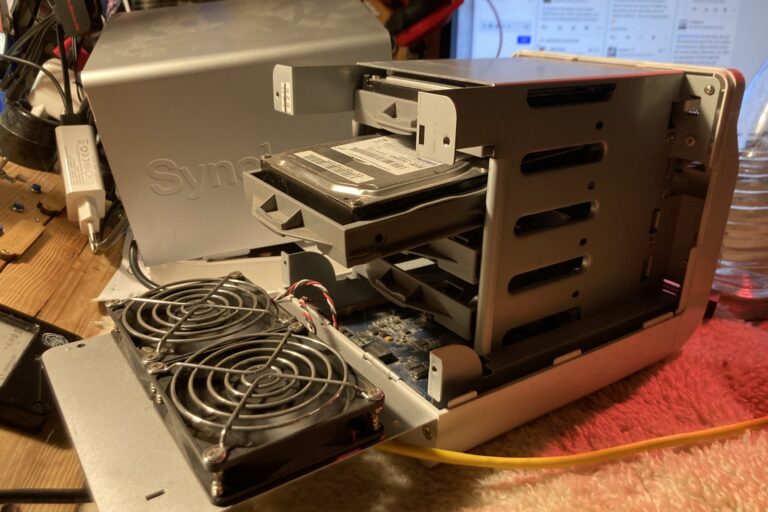
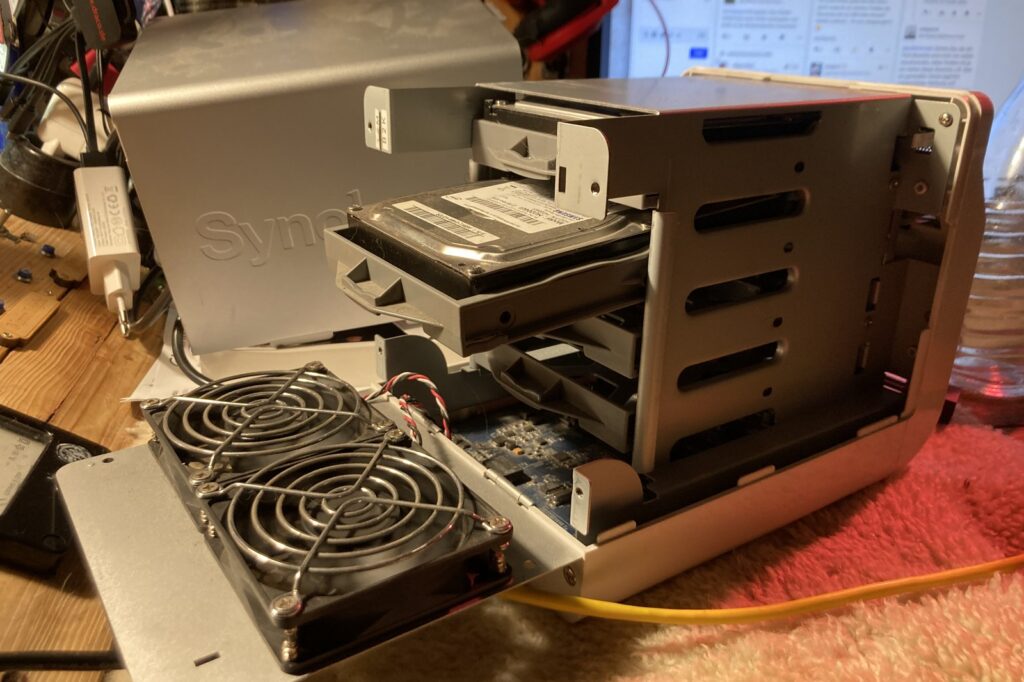
The flaw carries a CVSS score of 9.8 and allows remote code execution. Threat actors are exploiting this known flaw against devices running end-of-life versions of DiskStation Manager (DSM). Synology has released security updates, but users on outdated versions remain targeted. In a separate but related move, the vendor addressed PHP2Shell vulnerabilities affecting certain PHP-dependent packages. The practical upshot: any Synology user who has not updated their DSM software is sitting on a known, high-severity hole.
Healthcare has become a primary target. The University of New Mexico Health System diverted ambulances due to a ransomware attack on October 26, 2026. The incident forced the cancellation of appointments and limited new patient intake, though critical systems were restored within days. Michigan State University also felt the impact; the BYOD ransomware gang claimed to have stolen personal information on 1.3 million current and former students. The group, which emerged in September 2026, has previously targeted hospitals and, according to reporting, a mobile service associated with the Trump administration. The common thread is credential compromise—gaining access through stolen or weak passwords rather than complex exploits.
Ransomware-as-a-service is lowering the barrier to entry. Groups like BYOD operate on a model where the infrastructure and ransomware payload are available to affiliates, meaning actors with limited technical skill can launch campaigns. The practical result for ordinary readers is that everyday devices—home NAS units, university networks, hospital systems—are under pressure from campaigns that move quickly and strike during business hours.
The surge reflects a shift toward known flaws and credential theft rather than zero-day surprises. Patching remains the single most effective mitigation. Synology has urged users to upgrade to the latest supported DSM version and to apply PHP security updates through the Package Center. For healthcare and educational institutions, the incident response focus is on credential hygiene and network segmentation to limit the speed of lateral movement.
Sources
- Ransomware
- Ransomware Alert – Ransomware Attacks Targeting Synology NAS Devices
- Synology NAS Devices Targeted in Ransomware Attacks Exploiting Patched DSM Flaw
- University of New Mexico Health System Diverts Ambulances Due to Ransomware Attack
- Michigan State cyber incident claimed by ransomware gang behind recent hospital attack
- Quarterly Ransomware Operations Report
Photo: Korrupt (CC BY 4.0)