BERLIN, November 16, 2026 — The shift is in how we view municipal data security, and the massive Berlin Senate leak is a stark example. Over 5 terabytes of sensitive government files, from plaintext passwords to critical infrastructure material, were dumped on the dark web after a ransomware group’s extortion demand was rejected. This breach is a significant data failure in Europe, but what’s changing is the scale and the sophistication of the attack vector.
A Timeline of the Breach and Leak
The trend underneath this incident is a prolonged, targeted infiltration. For five days, from August 7 to 12, the attackers exfiltrated data. The breach was discovered on August 13 when a domain controller was disrupted, and officials confirmed the hack the following day. On August 14, two parts of the Senate administration were disconnected from the state network in a containment measure.
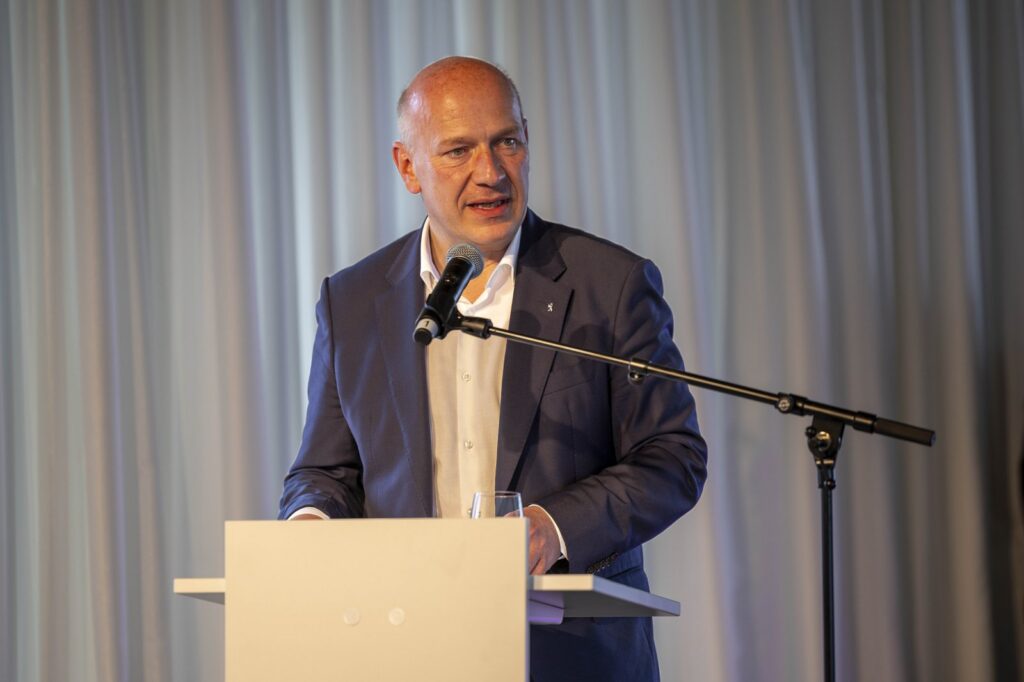
The extortion attempt followed, with Rhysida demanding 30 bitcoin—worth about €2 million at the time. Berlin Mayor Kai Wegner and Interior Senator Iris Spranger refused, stating, “The state of Berlin will not be extorted.” When the deadline passed on September 4, Rhysida made good on its threat, releasing the massive trove of data on the dark web for anyone to download.
The Method: A Phishing Campaign That Bypassed Defenses
Watch this space, because the attack method used by Rhysida is a concerning development. Germany’s Federal Office for Information Security (BSI) reported that the group gained access through an attack called TerminalFix. This was not a brute-force assault but a clever phishing campaign. It specifically targeted the Senate departments for Construction and Transportation using fake CAPTCHA pages. Victims were tricked into running PowerShell commands that downloaded malware, giving the attackers a foothold in the network.
The Scope of the Leak: What’s at Stake
The sheer volume of the stolen data is what makes this breach stand out. Rhysida claims the leak contains a wide range of sensitive materials, including plaintext passwords, legal and contract documents, financial records, personnel files, and regulatory offense records. Most alarmingly, it includes material related to critical infrastructure. The Senate Chancellery confirmed that data was exfiltrated from key departments, including Mobility, Transportation, Climate Action and the Environment, as well as Urban Development, Construction and Housing. For a city with a population of 3.7 million and a role as a global hub, the exposure of this information is a profound failure in public sector data management.
Systemic Vulnerabilities and What Comes Next
This leak highlights systemic vulnerabilities in how government entities manage and protect vast amounts of data. The fact that a phishing campaign could lead to a multi-terabyte data exfiltration from a capital city’s administration points to deeper issues in access controls and employee training. While German authorities, including the Federal Criminal Police Office (BKA) and the BSI, are analyzing the data, the damage is done. The data is now public, and its potential use for further attacks or espionage is a concrete reality. The next scheduled date for public updates from Berlin officials on their response remains to be seen, but the shift in municipal cybersecurity has already occurred.
Sources
- Berlin’s massive data leak: How to dissect it
- Berlin
- Dispatch from Berlin: What Germans most want to know about the post-midterms United States
- AYSW? | Learning Objectives in Teaching the Fall of the Berlin Wall
- 'Contextuality' (with apologies to Irving Berlin)
- RB Leipzig Hope Neil El Aynaoui Recovers In Time For Union Berlin Clash
Photo: Dr. Frank Gaeth (CC BY-SA 4.0)