
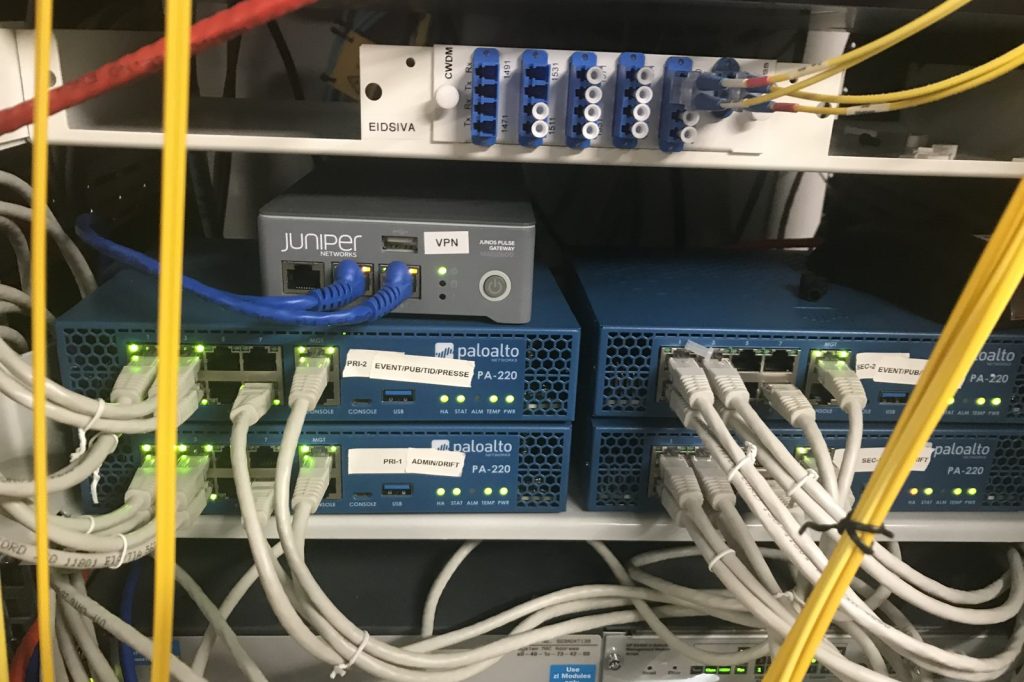
Palo Alto Networks says ransomware crews are still using a patched hole in its firewalls. The flaw is CVE-2026-0257, an authentication bypass in PAN-OS and Prisma Access rated 7.8 on the CVSS scale. Palo Alto fixed it in May 2026, and the U.S. Cybersecurity and Infrastructure Security Agency added it to its Known Exploited Vulnerabilities catalog on May 13. Patching, as ever, turns out to be optional for a good many networks.
What the attackers do with it
The bug lets an attacker set up an unauthorized VPN connection and slip past multi-factor authentication. Unit 42, Palo Alto’s research team, named two groups exploiting it: Spikey Scorpius, also known as Qilin, and Tarnished Scorpius, also known as INC. ReliaQuest said it had detected Qilin and the Settra group using the flaw in financially motivated attacks, and Arctic Wolf had flagged Qilin’s use of it back in July, with attacks ranging from fast encryption-only jobs to full double-extortion campaigns.
Once in, the intruders use remote monitoring and management tools to survey the internal network, move sideways over RDP and SMB, and stage tooling for harvesting credentials, stealing data and deploying ransomware. Unit 42 lists the targets as education, financial services, healthcare, high technology, hospitality, manufacturing, professional and legal services, government, transportation and logistics, utilities and energy, and retail.
Under the hood: the virtualization layer
The detail that matters is where they go next. Unit 42 called the direct pivot to the virtualization layer “the most significant evolution” in tactics after exploitation. In one case the attackers went from the compromised VPN gateway to the vCenter management appliance, disabled security controls on ESXi hypervisors, and used a custom tool to dump credentials offline from a domain controller’s virtual disk (VMDK). Because that happens beneath the guest operating system, it sidesteps endpoint detection tools running inside it, and it yields domain-wide credentials. Some attackers have also chained the initial access with attacks on Veeam backup infrastructure, abusing a known flaw, CVE-2023-27532, to do maximum damage.
The money
Ransomware payments hit a record $1.25 billion in 2023, then fell to $813 million in 2024, a drop attributed to victims refusing to pay and to law enforcement action. In 2025 the FBI’s Internet Crime Complaint Center logged 3,611 ransomware complaints with reported losses of more than $32 million. The FBI cautions that the figure leaves out costs such as lost business and remediation, and that some victims report no loss at all.
Besides applying the latest fixes, Palo Alto Networks recommends that organizations hunt for indicators of compromise and start incident response if they find successful gateway-connected events.
Sources
- Ransomware
- Global Ransomware Damage Costs Predicted To Reach $20 Billion (USD) By 2021
- Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA
Photo: DiFronzo (CC BY 2.0)




