The county started at $100,000. The attacker wanted $3 million. After about a month of haggling, a U.S. government entity paid roughly $1 million to keep stolen files off the internet, according to a case study by researcher Rakesh Krishnan for Ransom-ISAC.
Krishnan built his account from a leaked negotiation chat and the blockchain trail the payment left behind. The group on the other end calls itself Kairos. It may not be a ransomware gang at all. Krishnan found no sign it ever locked a single machine: no encryptor, no locker, no demand for a decryption key. It stole files and charged for silence.
The county behind the chat
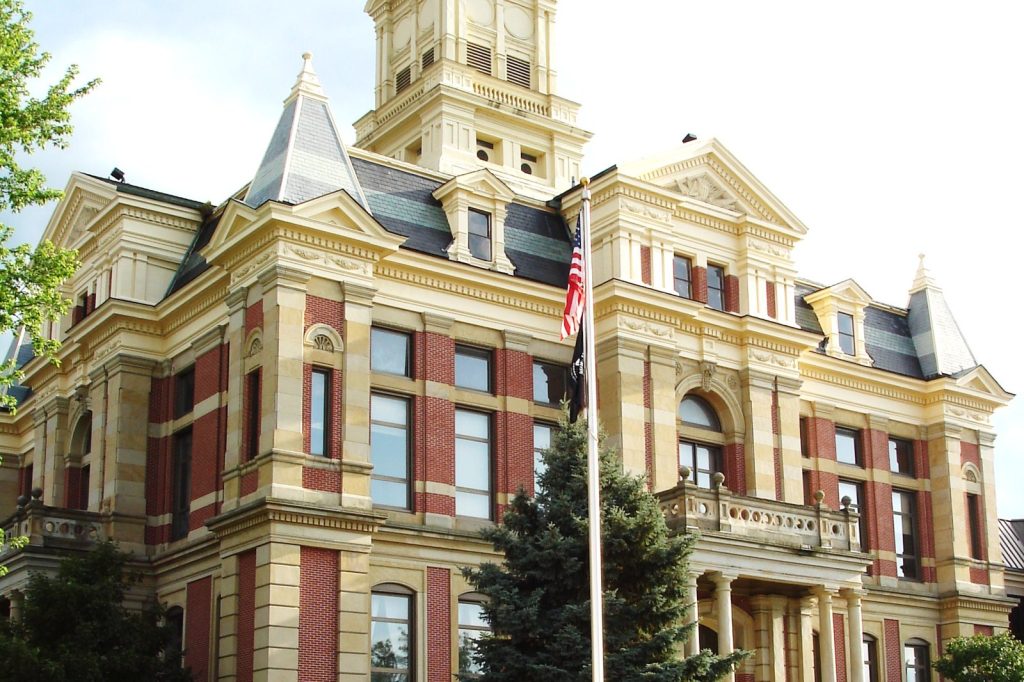
Krishnan does not name the victim, but the evidence points to Union County, Ohio. The proof-of-theft files carry names such as Union.xlsx and 1 union co psi template.doc, and the final archive was called union.rar. The victim describes itself as a small county with limited resources. The attacker leaned hard on one folder marked “prosecutors office,” warning that a leak would help criminals dodge charges.
It fits a real case. In May 2025 Union County said it had found ransomware on its network. It later told 45,487 residents and staff that their data had been taken, most of a county of roughly 70,000 people. Social Security numbers, financial details, fingerprints and passport numbers were among the records. Neither the county nor Kairos has confirmed the link, and The Hacker News has asked the Union County Commissioners’ Office for comment.
How the bargaining went
Kairos claimed more than 2 terabytes, some 1.6 million files. The county moved from $100,000 to $255,000, then $430,000. Kairos came down to $2 million, then named a final number: $1 million, paid by Friday, or the files go public. It used a countdown timer and threatened to dump the most sensitive folders first.
The county paid on June 13, 2025, ten times its opening offer. The payment was about 9.44 bitcoin. Within hours it was split in two and pushed through a chain of wallets toward deposit addresses tied to Bybit, OKX and a Russian service called BELQI. Tracing like that gives investigators leads, not names.
What did the money buy? Kairos sent a “proof of deletion” file. But a list of file names only shows the attacker once held the files, not that anyone wiped the originals.
Not an isolated case
Sophos reported in 2025 that only about half of ransomware attacks still involve encryption, the lowest rate in six years. Silent Ransom Group, a Conti offshoot, has run pure data-theft extortion against U.S. law and finance firms for years without an encryptor.
The Kairos haggling also echoes the leaked Black Basta chats of February 2025, where a $1.5 million demand and a $100,000 counter ended in a $1 million payment.
Kairos has gone quiet. Its leak site is down and its last known victim appeared in June 2026. A wallet tied to the operation was still moving money as recently as May 2026.
Kairos claimed it got in by guessing a password. The temp.sh links it used to move files are the kind of thing defenders can watch for, along with repeated failed logins and large outbound transfers.
Sources
- U.S. Government Entity Paid Kairos $1 Million in Data-Theft Extortion Case | Mallory
- U.S. Government Entity Paid Kairos $1 Million in Data-Theft Extortion Case
Sources
- Union County, Ohio Government Pays $1 Million Bitcoin Ransom to…
- U.S. Government Entity Paid Kairos $1 Million in Data-Theft… | Mallory