SYDNEY, November 4, 2026 — NSW Police’s Cybercrime Squad has opened a criminal investigation into an alleged data breach at NSW Health after being alerted at about 1 pm on Friday, October 30. The breach, declared a major incident by Cyber Security NSW, affected an isolated server with no patient data impacted or currently at risk, the agency said.
Strike Force Civic Leads Investigation
Detectives are working under Strike Force Civic in coordination with NSW Health and Cyber Security NSW, a police spokesperson confirmed. The strike force has now been invoked in three state government data incidents this year, including an April case involving a NSW Treasury staff member and a July charge against a NSW Health nurse for allegedly accessing patient records. Police have not stated whether Strike Force Civic operates as a standing unit for data misuse across agencies.
Threat Actor Claims Await Verification
A threat actor identified as ‘bytetobreach’ posted on an underground forum claiming to have exfiltrated roughly 70 gigabytes of unredacted documents — about 100,000 files — by exploiting a misconfigured subdomain. The actor said a broader network intrusion was halted when they accidentally crashed a targeted server. Hackmanac, a threat intelligence firm, said the claim remains pending verification. Cyber Security NSW confirmed investigations are underway but declined further comment citing the criminal probe. No ransom demand has been made; the actor wrote that none would be asked from anyone affiliated with the Australian government.
Ministers Stress Resilience Amid Growing Threats
NSW Health Minister Ryan Park said no patient details or clinical services have been compromised and described the agency’s cybersecurity systems as “very robust.” He acknowledged cyberattacks as a major challenge for governments at all levels. Transport Minister John Graham told ABC radio the incident serves as a wake-up call, adding that cyber security is becoming “increasingly difficult” for government, private companies, and citizens alike.
Public Sector Coverage Runs Through Self-Insurance Fund
New South Wales government agencies are insured via the Treasury Managed Fund, a self-insurance scheme administered by Insurance and Care NSW (icare) on behalf of NSW Treasury, rather than through commercial cyber policies. The fund is backed by a reinsurance programme that would engage private capital only for sufficiently severe losses. Insurance brokers note the current disclosures do not suggest this incident approaches that threshold. NSW agencies also report under the state’s Mandatory Notification of Data Breach scheme, which commenced in November 2023, not the federal Notifiable Data Breaches scheme that applies to private entities.
Health Sector Leads Breach Notifications Nationally
Federal data underscore why health exposures draw underwriting attention. The Office of the Australian Information Commissioner received 667 breach notifications between January and June 2026, with health service providers lodging 149 — the most of any sector — including 72 attributed to malicious or criminal attack. Breaches affecting more than one million people rose to 11 in that half, up from four in the prior period. Across 2025 the OAIC recorded 1,205 notifications, the highest since the scheme began in 2018, with health accounting for 225, or 19 per cent.
Previous Incidents Highlight Recurring Exposure
The alleged breach follows a March 2025 incident where an automated account downloaded more than 9,000 files from NSW JusticeLink, a platform handling sworn statements and identity information for over 400,000 court cases annually. In July 2026 a former NSW Health employee was charged for allegedly downloading patient records without authorisation. Another 2025 incident exposed data of nearly 600 medical staff after confidential documents were left publicly accessible online. The current investigation remains active with no cause attributed.
Sources
- NSW Health server targeted in cyber incident
- Cybercrime squad investigating 'major' NSW Health data breach
- Hacker claims 100,000 documents stolen from NSW Health
- Major cyber breach declared at NSW Health
- NSW Health cyber breach puts public sector cover in focus
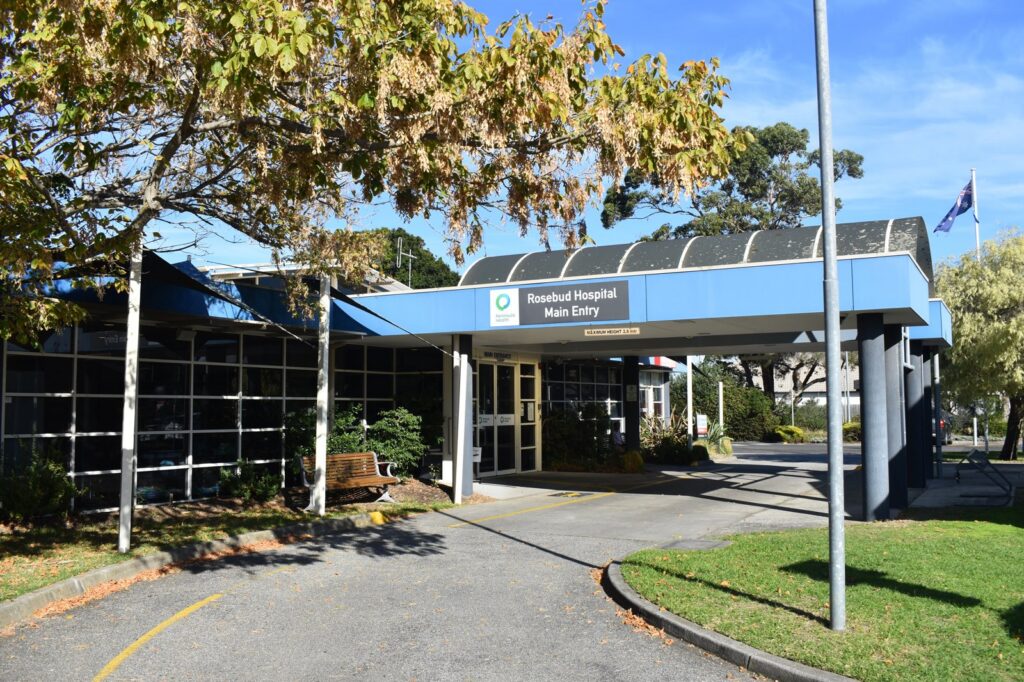
Photo: Alison Newman (CC BY-SA 4.0)