
LONDON, July 25 — The UK National Cyber Security Centre in March 2023 disclosed a sustained hacking campaign by the Russian state-sponsored group known as Cold River, which had targeted nuclear fusion research organisations in the United Kingdom, the United States and NATO member states.
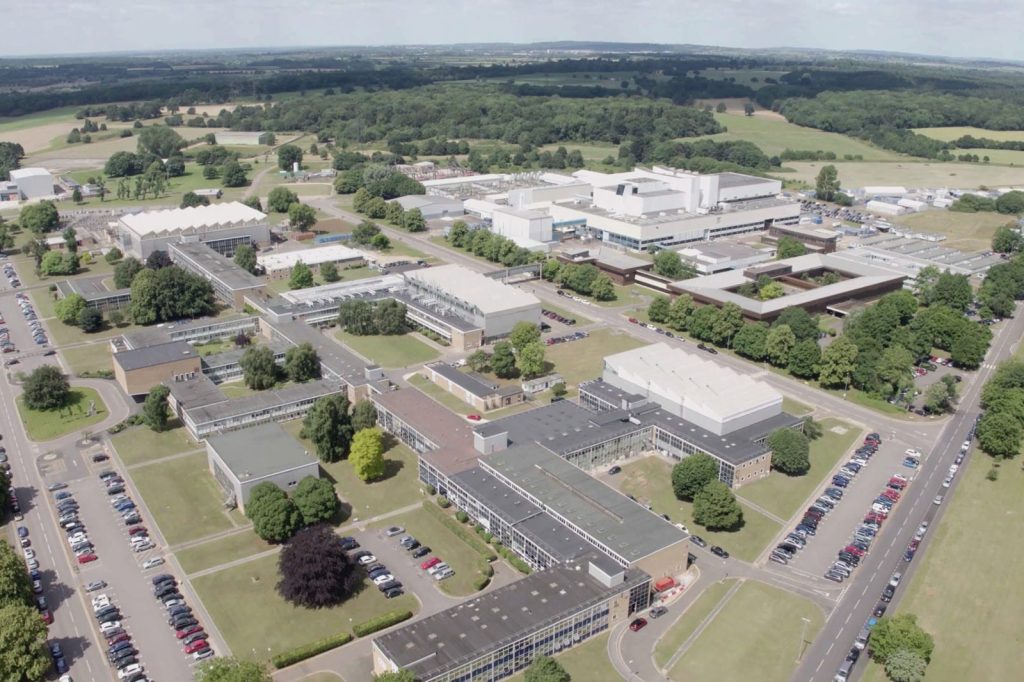
According to the disclosure, the group — also tracked under the designations Callisto, TA446, SEABORGIUM and Star Blizzard — focused its attacks on the UK Atomic Energy Authority, which operates the Joint European Torus at the Culham Centre for Fusion Energy, as well as on other fusion laboratories and private companies involved in fusion energy development. The record shows that Cold River employed spear-phishing emails, credential theft and custom malware to compromise email accounts and network systems.
Officials confirmed that the campaign aimed to steal intellectual property related to nuclear fusion technology, including reactor design, plasma confinement methods and materials science data critical for the development of clean energy. The UK government, in January 2022, had already imposed sanctions on three Russian individuals for attempted interference in UK political processes, and the fusion-hacking revelations prompted further diplomatic measures from London.
On 28 March 2023, the US Department of Justice unsealed an indictment charging six officers of the Russian Main Intelligence Directorate’s Unit 26165 in connection with a separate but related cyber campaign that had targeted energy and nuclear facilities worldwide. The indictment, filed as United States v.
Mrikhin et al., case 1:23-cr-00110, detailed multiple conspiracy counts including computer fraud, wire fraud and identity theft. The hacking campaign had been monitored by cybersecurity firms Mandiant and Microsoft, which attributed the activity to Russian intelligence services. The indictment underscored the breadth of Russian state-sponsored cyber operations against critical infrastructure and sensitive scientific assets.
The Strategic Context
The attacks underscore the vulnerability of high-value scientific networks to state-sponsored cyber espionage and the strategic importance of fusion energy as a geopolitically sensitive technology. The theft of intellectual property related to reactor design and plasma confinement methods represents a direct threat to long-term energy security for Western nations. The UK NCSC’s public disclosure and the parallel US indictment together paint a picture of coordinated intelligence-collection efforts targeting the frontier of clean-energy research.
Observers note that the targeting of both government-operated facilities such as the UKAEA and private companies involved in fusion development indicates a comprehensive espionage strategy. The case also highlights the persistent overlap between political interference operations — for which the UK had previously sanctioned Russian individuals — and cyber-espionage campaigns directed at scientific and industrial targets.
The attribution by Mandiant and Microsoft provided the technical trail that underpinned both the UK diplomatic response and the US criminal charges. Going forward, the fusion-energy sector remains a prime target for state-backed hacking groups seeking to acquire proprietary research, and the precedent set by the Cold River campaign is likely to inform defensive measures across the allied research infrastructure.




