The n0n ransomware gang has published a 500MB dataset allegedly stolen from Expedia, exposing millions of customer records after negotiations with the travel giant reportedly failed.
What the Hackers Leaked
Cybernews researchers found the dumped data contains a comprehensive breakdown of customer information. The archive includes approximately 150,000 consumer account records with email addresses dating from 2011 to 2018. Researchers also identified 100,000 booking order events from 2018, containing booking confirmations and customer email addresses.
The leak extends to loyalty programs, with around 400,000 loyalty program account records exposed, containing program details and plan names. The data also includes approximately 200,000 cruise passenger emails, with a filename indicating they are dated October 2024. Additionally, researchers found around 500,000 fraud evaluation records containing email addresses and associated statuses.
To connect the various datasets, the archive includes about 350,000 reference records. Around 120,000 traveler profiles and approximately one million records describing estimated customer spending patterns on accommodation, car rentals, and other travel services were also part of the dump. The technical reality of the breach is further complicated by the inclusion of old account credentials and bcrypt password hashes, posing a significant account takeover risk.
The Attackers and Their Demands
The n0n ransomware gang first listed the US travel technology giant Expedia on its dark web leak site in early October, initially claiming to have stolen one billion records. As ever, the detail that matters is that the group appears to have moved from extortion to public exposure following a breakdown in negotiations. The gang has also recently listed Visa and JPMorgan Chase as alleged victims, though Visa has confirmed the incident involved a third-party provider in Asia Pacific, not its core systems or payment data. JPMorgan Chase has stated its recent service outage was caused by a software bug and has no evidence of a cyberattack.
Heightened Risks for Travelers
The exposure of this data creates a serious privacy nightmare for impacted users. The compromised information provides criminals with a treasure trove of sensitive details that could be leveraged for targeted social engineering campaigns. Travelers’ emails and booking information enable scammers to build detailed profiles of individual victims and target them with convincing phishing messages. Attackers can send messages pretending to come from Expedia, hotels, airlines, or cruise operators, using the specific details from the leak to make their scams more believable.
Forgotten accounts pose a particularly high risk. Customers who set up Expedia accounts years ago may have never updated their passwords. If those credentials were reused across other services, attackers could gain unauthorized access to unrelated accounts. The bcrypt password hashing algorithm, while designed to make password cracking more difficult, still means the stolen hashes are a target for attackers attempting to recover the original passwords.
Expedia’s Silence
Expedia has not confirmed the alleged breach, and Cybernews is awaiting a response. The company operates some of the world’s best-known travel platforms, including Expedia, Hotels.com, Vrbo, Travelocity, Orbitz, Hotwire, and Trivago, generating nearly $5 billion in revenue and connecting millions of travelers with services globally.
Sources
- Expedia data leak exposes millions of travel records
- Visa confirms security incident, JPMorgan knocked down
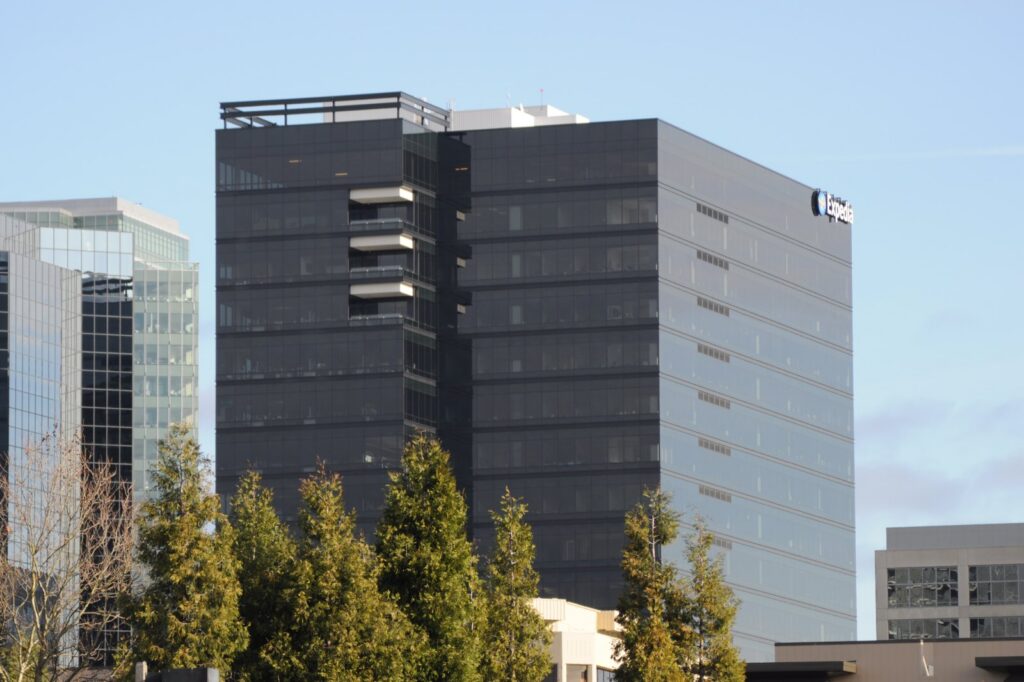
Photo: Joe Mabel (CC BY-SA 3.0)