“I have a hard time believing terabytes of FBI personnel data just sit on a shelf.” That was Denis Calderone, chief technology officer at Suzu Labs, on the latest boast from ShinyHunters, the hacking group now claiming it has gutted the FBI’s recruitment and personnel records.
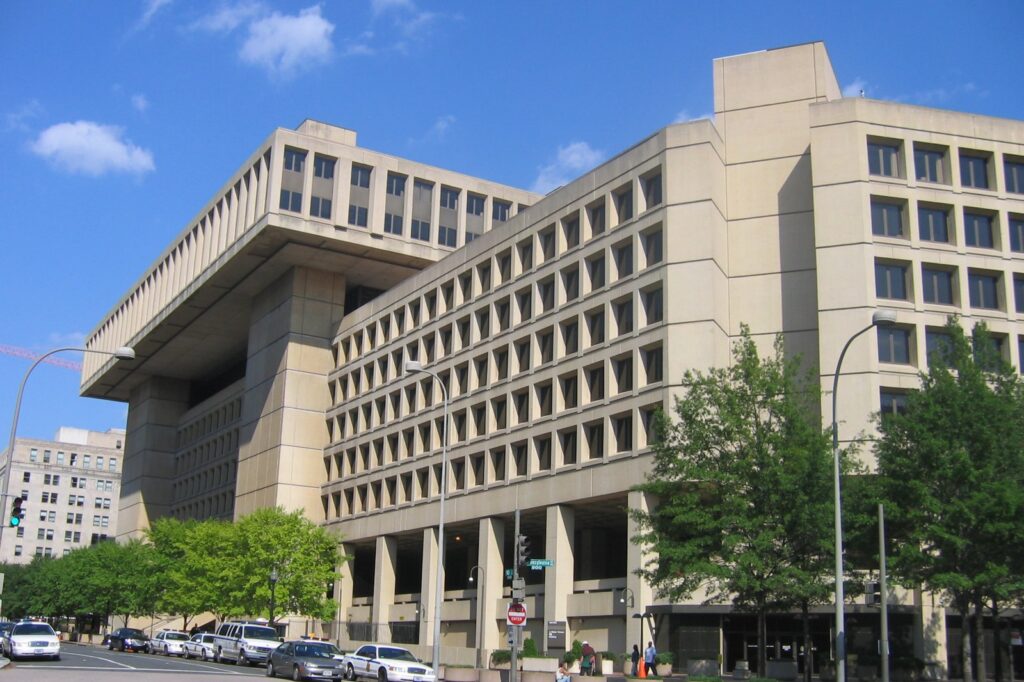
The FBI said on September 22 that it was investigating the group’s claim to have stolen data on thousands of current and former agents. Axios reported the next day that the haul exceeded 2 terabytes and covered “almost all FBI agents and individuals who filed an application with the FBI for a job.”
How the group says it got in
404 Media broke the story. It reported that the hackers used a zero-day flaw on an Oracle PeopleSoft human resources server, then pivoted into an Amazon-hosted government cloud holding the agents’ and applicants’ records.
The demand is odd. Instead of a ransom, ShinyHunters wants the FBI to take down a report from last May that the group says contains false information about it. Calderone thinks that gets the FBI nowhere. “The FBI isn’t going to pay, and it isn’t going to pull an advisory because a criminal group demanded it,” he said, adding that he doubted the bureau would act on the threat.
The week had been busy for the group. Calderone said that on Friday it took over the Clop gang’s leak site and posted a “seized by ShinyHunters” banner, and by Tuesday the same banner appeared on the FBI’s jobs portal. The vx-underground account posted about the defaced portal on September 22. Calderone described both moves as payback, one for threats from a rival gang and one for an FBI advisory telling victims not to pay.
What is not proven
Collin Hogue-Spears, senior director of solution management at Black Duck, urged caution. The sample ShinyHunters posted, he noted, does not show where the records came from, when they were taken, or whether they came from FBI systems at all. The group has produced no public evidence of access to the FBI’s internal HR system or FBINet, and the FBI, Oracle and AWS have not confirmed its claims.
Calderone’s worry is practical. Foreign intelligence services would love the data, he said, and a group that can say it hit the FBI makes every later extortion demand more believable. If the PeopleSoft zero-day is real, the exploit may be worth more than the data. Agents and their spouses, he warned, could see home addresses posted publicly within a week if the threat is followed through.
Hogue-Spears drew a lesson for everyone else. Internet-facing recruiting portals should be narrow intake systems, with permission to submit applicant records and none to retrieve employee data, and public access to PeopleSoft management interfaces such as /PSEMHUB/ should be blocked. A compromised FBI workload would not automatically amount to an AWS breach, he said, but excessive permissions or exposed administrative functions can turn a public job portal into a path to the HR system behind it.