
Understanding the Gap Between Capability and Intent
At its heart, the debate is about the chasm between capability and intent. Capability means a state has the tools and access to potentially interfere with an election. Intent means it decided to use those tools. Intelligence analysis treats these as separate questions, and blurring them together, officials warn, produces misleading conclusions. The capability warning is a reason to harden defenses — to invest in paper trails, post-election audits and network security — not evidence that an election was actually altered.
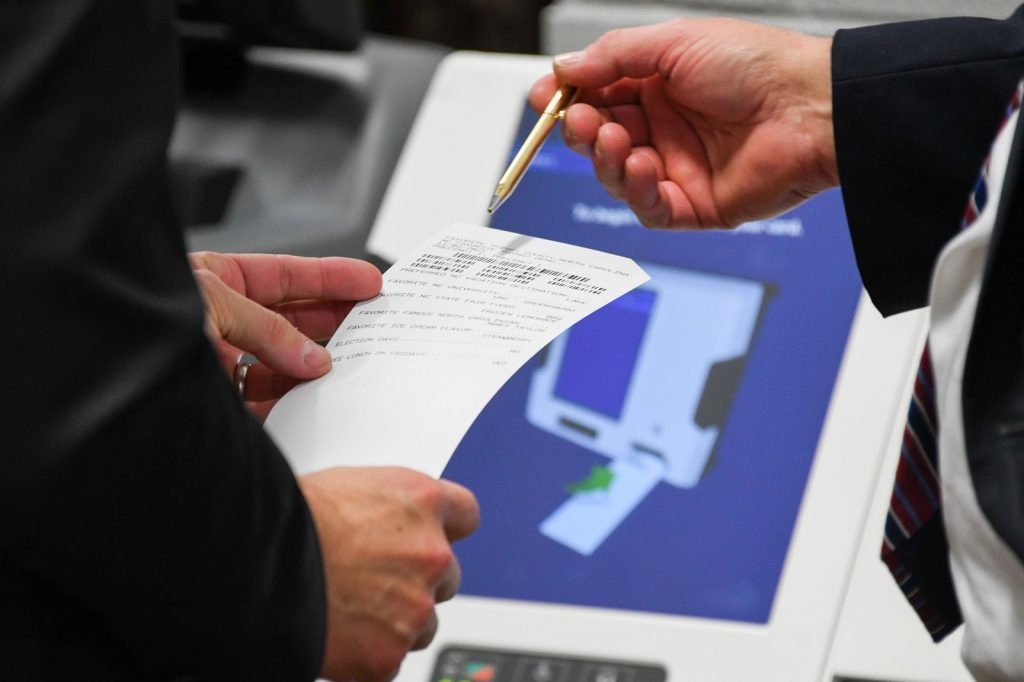
Election cybersecurity, or election security, refers to the protection of elections and voting infrastructure from cyberattack or cyber threat. This includes protecting against tampering with or infiltration of voting machines and equipment, election office networks and practices, and voter registration databases. Cyber threats or attacks to elections or voting infrastructure could be carried out by insiders within a voting jurisdiction, or by a variety of other actors ranging from nefarious nation-states to organized cyber criminals to lone-wolf hackers. Motives may range from a desire to influence the election outcome, to discrediting democratic processes, to creating public distrust or even political upheaval.
A variety of experts and interest groups have emerged to address voting infrastructure vulnerabilities and to support democracies in their security efforts. From these efforts have come a general set of policy ideas for election security, including transitioning from black-box proprietary voting systems to transparent open-source voting systems, implementing universal use of paper ballots marked by hand and read by optical scanner to ensure a voter-verified paper audit trail, and passing voter machine certification requirements that phase out touch-screen voting machines, especially the most vulnerable direct-recording electronic devices. Other best practices include verifying voting results through risk-limiting audits, ballot accounting and reconciliation, giving voters an opportunity to fix mistakes on their ballots, banning electronic voting, securing all voting infrastructure using cyber hygiene tools such as the CIS “20 Critical Security Controls” or NIST’s Cybersecurity Framework, and designating elections as critical infrastructure with appropriate funding for upgrades and audits.
The Intelligence Community’s 2020 Election Assessment
What unfolded in the months after that January 2020 warning is where the real story lies. On January 7, 2021, the Intelligence Community delivered its assessment on the 2020 election itself. That report, declassified on March 16, 2021 and available at dni.gov, assessed with high confidence that China did not deploy interference efforts to change the outcome. This was the majority judgment, the formal finding of the intelligence community.
Not everyone agreed. Then-DNI John Ratcliffe, and later DNI Tulsi Gabbard, argued that China’s role was understated. This is a documented dissent, a matter of record. But it is a dissent — a disagreement over emphasis and analytic judgment, not proof of a Chinese operation. For those involved in the debate, the distinction matters enormously. The majority finding stands: capability is not the same as action.
For readers trying to make sense of the headlines, the takeaway is precise. A warning that an adversary could interfere is a call to vigilance, not a verdict on the past. The four named states remain a concern, and the investment in election security continues. But the evidence on 2020, as assessed by the intelligence community, is clear: China did not act to change the outcome. The dissent is real, but it is a dissent, not a counter-finding.
Looking Ahead: How This Distinction Shapes Future Debates
What to watch next is how this distinction shapes the next round of election security debates. With the capability warning now declassified, the question of intent — and of how to prove it — will remain at the center of the conversation. For those who track these issues, the difference between what a state can do and what it did do is not a technicality. It is the whole story.
Pre-election logic and accuracy testing to check for equipment malfunctions, instituting a pre-election threat assessment plan to bolster technical support capacity for election officials requesting assistance, and calling upon outside experts to conduct cyber assessments — including government specialists and white-hat hackers — remain key components of ongoing efforts to secure the nation’s voting infrastructure. As the debate continues, the distinction between capability and intent will remain central to understanding both the threats facing American elections and the appropriate responses to them.
Sources
{“@context”: “https://schema.org”, “@type”: “NewsArticle”, “headline”: “Capability and intent gap central to election cybersecurity debate”, “description”: “Understanding the Gap Between Capability and Intent At its heart, the debate is about the chasm between capability and intent. Capability means a state has…”, “datePublished”: “2026-07-16T09:30:00+00:00”, “author”: {“@type”: “Person”, “name”: “Henry Thomas”}, “publisher”: {“@type”: “Organization”, “name”: “InfoPulse Today”, “url”: “https://newsfeed.infopulsetoday.com/”}, “citation”: [{“@type”: “CreativeWork”, “url”: “https://en.wikipedia.org/wiki/Election_security”}, {“@type”: “CreativeWork”, “url”: “https://www.dni.gov/files/ODNI/documents/assessments/ICA-declass-16MAR21.pdf”}]}




