Synology’s Patch Problem: Why Old Vulnerabilities Still Win
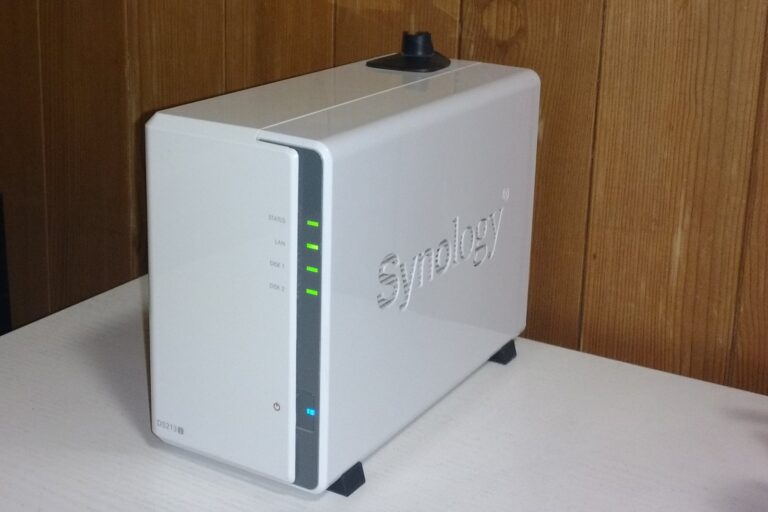
Synology has issued a security advisory warning that C3RB3R ransomware is encrypting files on DiskStation Manager installations that were never brought up to date, and the company’s own account of the entry point is a case study in why patching discipline matters more than patch availability. The advisory, tracked as Synology-SA-24:20, covers three vulnerabilities disclosed after Pwn2Own 2024, and Synology’s October 29 statement points to a flaw patched in December 2024 as the one the attackers are using.
The detail that matters here is not the ransomware’s encryption routine, competent as it is. It is the gap between the day a fix shipped and the day a device was actually updated. Synology’s advisory lists fixed releases including DSM 7.2.2-72806-1, 7.2.1-69057-6, 7.2-64570-4, 7.1.1-42962-7 and 6.2.4-25556-8, and the company recommends enabling automatic updates and blocking internet access to the management web interface. Those are the two controls that would have stopped this campaign cold on most boxes.
What the Attackers Actually Exploit
The three flaws in SA-24:20 are not exotic. CVE-2024-10441 carries a CVSS score of 9.8 and allows unauthenticated remote code execution without user interaction. CVE-2024-50629, a webapi flaw, lets a remote attacker read limited files, and CVE-2024-10445, a certificate validation bug, lets an adjacent attacker write limited files. Those two score 5.3 and 4.3 respectively. The 9.8 is the one that turns a reachable management interface into a foothold.
Public reporting has not established which individual vulnerability was used in each incident, or whether attackers combined them. There is a tidy explanation for why a two-year-old bug would suddenly be in active use: on October 25, a public writeup and proof of concept for the 2024 flaw appeared on GitHub, four days before both advisories. A working exploit for an old flaw turns every unpatched box into a target overnight.
Not everyone agrees on the entry point. Security firm 360 attributes the incidents it investigated to two flaws disclosed on September 18, 2026, CVE-2026-13639 and CVE-2026-13684, both rated 9.8 and stemming from insufficient entropy in login logic and inadequate SCGI output encoding. Synology explicitly rules out the recently patched PHP2Shell bugs and says its investigation shows the campaign exploits only the flaw addressed in SA-24:20. A response team identified as Solar reports one affected NAS already running a recent DSM 7.4.1 build, which would not fit the 2024 theory, and does not rule out add-on packages, containers or stolen credentials. No proof of a zero-day has been published.
Under the Hood of C3RB3R
The analyzed sample skips 27 system directories and several file categories, then walks everything else recursively. It generates a 256-bit key per file, encrypts with ChaCha8 and wraps that key with RSA-2048. A list of 187 priority extensions gets full encryption, while other files are partly encrypted to shorten the run. Every encrypted file picks up the .L0CK3D suffix, and each folder receives a read-me3.txt with a six-digit ID and a Tor address.
The demand starts at 0.036960 bitcoin, roughly $2,952, and doubles after five days to 0.073920 bitcoin, about $5,904. The note warns that restoring files with third-party software will be “fatal” and offers to decrypt one file free as proof. Backups stored on the same box go with everything else, which is the part that catches home users and small offices who treat a NAS as both primary storage and backup.
Reports of unreadable files have come from South Korea since around October 28, with users filing damage reports to the Korea Internet & Security Agency. KISA acknowledged the reports but declined to describe scale, and nobody has produced a victim count. Synology did not issue a separate warning as damage mounted overseas, only disclosing the attack on its official website and recommending a security update. It guided users to restore locked files from existing backups and provided no decryption tool or compensation plan.
The Lesson for Anyone Running a NAS
Synology rarely issues advisories warning of attacks on its customers’ devices. The last such alert came in August 2019, after large-scale brute-force attacks led to eCh0raix ransomware infections. That seven-year gap is a useful reminder that NAS appliances sit on the internet with management interfaces, package ecosystems and third-party components, and they are attacked accordingly.
The technical reality of defending against patched-vulnerability ransomware is unglamorous. Install the latest DSM release your model supports, not the historical threshold from an advisory. Update official packages and third-party components. Turn on automatic updates so the next disclosure does not depend on someone reading a security notice. Block access to the management web interface from the internet, which removes the reachability that CVE-2024-10441’s 9.8 score assumes. Keep at least one backup copy offline or on a separate system, because a backup on the same encrypted box is not a backup.
The attribution dispute changes none of that. Whether the entry point was the 2024 flaw or the September 2026 pair, the remedy is the same and the deadline is not theoretical: the ransom doubles after five days, and the note in every folder makes the countdown explicit.
Sources
- Hackers Exploit Patched Synology NAS Vulnerabilities to Deploy C3RB3R Ransomware and Encrypt Files
- Synology warns of C3RB3R ransomware attacks targeting NAS devices
- Synology NAS Ransomware Alert: C3RB3R Locks Files W/ .L0CK3D
- Ransomware 'C3RB3R' Hits Synology NAS: 3.9 Million Won in Bitcoin Demanded, No Fix Beyond Patching — BigGo Finance
- Ransomware hits Synology NAS in Korea, demands bitcoin as damage spreads
- Synology NAS Ransomware: C3RB3R and DSM Security Gaps
Photo: Fabian sigrist (CC BY-SA 4.0)